Legal Intelligence · Privacy & Data Protection

Privacy & Data Protection legal & regulatory updates

Briefly tracks privacy & data protection developments — court rulings, legislation, gazette notices, and regulatory updates — from courts and regulators. 57 updates tracked in the past 30 days, last updated 31 Oct.

Get Privacy & Data Protection updates in your inbox
Legal News
Nigeria
Legal News

Nigeria Immigration Service: Kemi Nandap Directives on Efficiency

Comptroller General Kemi Nanna Nandap of the Nigeria Immigration Service (NIS) in Nigeria recently directed all personnel to eliminate service delivery delays and promptly report suspected cyber threats, as part of measures to enhance customer service and digital security. This directive underscores a dual focus on administrative efficiency and digital security within a critical government agency, impacting both public service delivery and national security. For businesses and individuals interacting with the NIS, it signals an expectation of improved service and a heightened awareness of data protection, potentially streamlining processes while also demanding greater vigilance against digital vulnerabilities. The emphasis on reporting cyber threats also highlights a proactive stance against evolving digital risks that could compromise sensitive data and operational integrity. The NIS operates under the Immigration Act, 2015, which governs its functions, powers, and responsibilities, including border control, issuance of travel documents, and enforcement of immigration laws. The directive on cyber threats aligns with broader national cybersecurity frameworks, such as the Cybercrime Act, 2015 (and its subsequent amendments), which mandates reporting of cyber incidents and establishes penalties for cyber offenses. Furthermore, the directive touches upon principles of administrative law, emphasizing accountability, transparency, and efficiency in public service delivery, which are fundamental tenets of good governance. The primary party involved is the Nigeria Immigration Service (NIS) and its Comptroller General, Kemi Nanna Nandap. The directive directly affects all NIS personnel, requiring them to adhere to new standards of service delivery and security protocols. Indirectly, all individuals and entities requiring immigration services in Nigeria, including foreign nationals, businesses, and legal practitioners, are impacted by these operational changes. Attorneys advising clients on immigration matters should anticipate potentially faster processing times for applications and services, while also being aware of the NIS's increased vigilance regarding digital security. Businesses, particularly those handling sensitive data or engaging in cross-border operations, should review their internal cybersecurity protocols to ensure compliance with national standards and to mitigate risks associated with potential cyber threats that could impact their interactions with government agencies. The directive highlights a growing emphasis on digital integrity within government operations, which could lead to more stringent data security requirements in future interactions and a need for practitioners to stay abreast of evolving digital compliance standards.

31 Oct
Burkina Faso
Legal News

Burkina Faso: Le Faso Digital 2026 Innovations Unveil 3 Key Civic Tech Projects

In Burkina Faso, FasoDonnées, FasoDoc, and Gundo Dev RNM Explorer have recently proposed digital innovations aimed at enhancing citizen access to public services, as part of the second edition of the Le Faso Digital initiative. These three initiatives, selected in the "Gouvernance, services publics et civic tech" category, seek to bridge the gap between citizens and public services through digital means. Specifically, FasoDonnées, FasoDoc, and Gundo Dev RNM Explorer aim to make public decisions more accessible, enable citizens to store essential identity and medical documents on their phones, and provide a platform to consult officially recognized professions within Burkina Faso. This represents a concerted effort to leverage technology for improved public administration and citizen engagement, aligning with the nation's broader digital transformation agenda. For legal practitioners in Burkina Faso, these developments signal a significant shift towards digital governance, impacting areas such as administrative law, data protection, and public information access. The move to digitize identity and medical documents raises critical questions regarding data security, privacy rights under existing or nascent data protection laws, and the legal validity of digital documents. Furthermore, increased accessibility to public decisions and professional registries could enhance transparency and accountability, potentially leading to new avenues for administrative challenges or public oversight, and requiring businesses to adapt to a more transparent regulatory environment. These initiatives operate within the broader framework of Burkina Faso's digital transformation strategy, exemplified by the "Le Faso Digital" program itself, which aims to modernize public services and foster innovation. While the excerpt does not detail specific statutes, such digital projects typically necessitate adherence to national data protection laws (e.g., Law N° 010-2013/AN on the protection of personal data), administrative procedure acts governing public information, and potentially new legislation or regulations concerning digital identity and electronic signatures. The legal validity and security protocols for storing sensitive personal and medical information on mobile devices will be paramount, requiring careful consideration of existing legal frameworks and potential legislative amendments to ensure compliance and citizen trust. Attorneys should closely monitor the legislative and regulatory developments stemming from these initiatives, particularly concerning data privacy, cybersecurity standards for public digital platforms, and the legal recognition of digital documents. Businesses, especially those in the tech sector or those providing services to the public, must prepare for an increasingly digitized administrative landscape, ensuring compliance with evolving data handling requirements and understanding the implications for contractual and administrative interactions. Furthermore, practitioners should advise clients on the potential for enhanced transparency and the legal implications of greater public access to government decisions and professional information. The outcome of these specific proposals is not yet reported, but their selection indicates a clear policy direction towards digital public service delivery.

31 Oct
India
Courtroom Update

Kerala Court Reprimands Police: Minor Identity Disclosure Failure

A sessions court in Kerala on Saturday criticized the police for failing to act against social media posts revealing the identity of a minor accused in a fatal car accident, specifically a 17-year-old son of an additional district judge, who allegedly drove under the influence and killed a scooterist on October 25. This judicial intervention highlights the judiciary's unwavering commitment to protecting the identity of children in conflict with the law, even when public sentiment might be against such protection, and underscores the police's fundamental responsibility in enforcing these statutory safeguards, particularly in the pervasive digital sphere. The court's strong stance signals a potential judicial directive for more proactive cyber policing and enforcement of privacy provisions concerning minors, setting a precedent for how such cases are handled in the age of social media. The core legal framework underpinning this matter is Section 74 of the Juvenile Justice (Care and Protection of Children) Act, 2015, which strictly prohibits the disclosure of a child in conflict with law's identity without the explicit permission of the competent authority. The sessions court, functioning in its capacity as a children's court, questioned the cyber police's inaction, implying an expectation of diligent enforcement of this statutory mandate. The case involves the Ernakulam Additional District and Sessions Judge Kavitha Gangadharan, the Kerala Police (specifically the cyber police), the minor accused, and the deceased scooterist, Jayabalakrishnan. For practising attorneys, particularly those representing minors in conflict with the law, this development serves as a critical reminder to be exceptionally vigilant about identity protection and to be prepared to seek immediate judicial intervention against any breaches, especially those occurring on social media platforms. Law enforcement agencies are now on clear notice regarding their duty to enforce Section 74 of the JJ Act, and businesses operating social media platforms may face increased pressure to comply swiftly with takedown requests related to such disclosures. The outcome of the court's order directing the police to submit a report on the action taken is not yet reported, and practitioners should monitor this closely for further guidance on enforcement mechanisms.

31 Oct
India
Case Law

MeitY: Developing Policy for Court Proceedings Recordings Use

In India, the Ministry of Electronics and Information Technology (MeitY) is formulating a policy to address the unauthorized use of court proceedings, as informed to the Supreme Court on Friday by Solicitor General Tushar Mehta. This development follows interim orders from the Supreme Court restricting the sharing of audio and video recordings of court proceedings on social media and digital platforms without prior permission. The initiative stems from a Public Interest Litigation (PIL) filed by Harshita Grover, which alleged that clips from live-streamed hearings were being edited, taken out of context, and widely disseminated online, leading to a distortion of judicial proceedings. The Supreme Court, through a bench led by CJI Surya Kant, had previously directed the Union of India to formulate guidelines, and MeitY is now actively engaged in this process, having received suggestions from various High Courts. The Court had also clarified in August that while news outlets could report on proceedings, they were prohibited from utilizing audio or video clips in their reportage. This initiative is profoundly significant for maintaining the integrity of judicial proceedings and shaping the public perception of justice in India. It aims to establish a crucial balance between promoting transparency through live-streaming and preventing the misuse or misrepresentation of judicial content. For legal professionals, it highlights the rapidly evolving regulatory landscape concerning digital content and the potential implications for intellectual property rights related to court proceedings. The forthcoming policy will likely set clear boundaries for the use of court-generated content, impacting media organizations, legal tech platforms, and individuals alike, underscoring the judiciary's proactive role in adapting to technological advancements while safeguarding its sanctity. The legal context for this development involves the Supreme Court's inherent powers to regulate its own proceedings and ensure the fair administration of justice, alongside the broader framework of information technology law in India. The PIL mechanism allows for critical public interest issues to be brought before the highest court. The interim orders and the anticipated MeitY policy will likely draw upon principles of copyright law, privacy rights, and the imperative to prevent contempt of court or defamation. MeitY's involvement suggests a regulatory approach that will likely leverage the Information Technology Act, 2000, and its associated rules, particularly concerning intermediaries and content regulation. The key parties involved are the Supreme Court of India (specifically the bench led by CJI Surya Kant), the Ministry of Electronics and Information Technology (MeitY), Solicitor General Tushar Mehta, and the petitioner Harshita Grover. Attorneys and legal professionals should closely monitor the development and finalization of MeitY's policy, as it will directly impact how court proceedings can be reported, analyzed, and shared digitally. Practitioners advising media houses, social media platforms, or individuals involved in legal commentary must thoroughly understand the new restrictions and permissions. Businesses that rely on public court records or live-streamed content for analysis or reporting will need to review and potentially update their compliance frameworks. Furthermore, legal professionals should be acutely aware of the Supreme Court's existing interim directives regarding the non-consensual sharing of audio/video recordings and advise clients accordingly to avoid potential legal repercussions, including contempt of court. The outcome of this matter is not yet reported, as the policy is still under formulation.

30 Oct
European Union
Legal News

Dutch Government Warns: EU Kids Act Privacy Risks for Children

The Dutch government has issued a warning regarding potential privacy risks within the proposed EU Kids Act, specifically cautioning that an 'excessive reliance on parents' could inadvertently create inequalities among children. This warning carries substantial legal significance for policymakers, technology companies, and legal professionals engaged in children's online safety and data privacy. It highlights the intricate challenge of balancing parental oversight with children's fundamental individual rights, particularly their right to privacy, as articulated in international instruments like the UN Convention on the Rights of the Child and the EU's General Data Protection Regulation (GDPR). The Dutch government's position suggests a preference for a more nuanced regulatory approach that empowers children while ensuring their protection, rather than exclusively depending on parental consent or control, which could inadvertently disadvantage children from less digitally literate or supportive family environments. This intervention could shape the final form of the EU Kids Act significantly. The EU Kids Act is an emerging piece of EU legislation likely designed to enhance online safety and privacy protections for minors, potentially building upon or complementing existing frameworks such as the GDPR and the Digital Services Act (DSA). The GDPR already establishes stringent standards for data protection, including specific provisions for children's data, such as Article 8 concerning children's consent in relation to information society services. The Dutch government's concern about 'excessive reliance on parents' directly addresses the interpretation of the 'age of digital consent' and the appropriate extent to which parental consent should serve as the sole gateway for children's online activities, especially regarding the processing of their personal data. The warning about 'inequalities' also invokes core principles of non-discrimination and equal access to digital services, which are fundamental rights within the EU legal order. Key parties involved in this legislative debate include the Dutch government, which has raised these critical concerns, and the European Union's legislative bodies responsible for drafting and adopting the EU Kids Act. Children are the ultimate beneficiaries and subjects of this act, while tech companies and online service providers represent key stakeholders who will be required to implement its provisions. Parents are also central to the discussion, as their role in children's online lives and data governance is a primary focus of the proposed legislation. The outcome of this legislative debate, specifically the final provisions of the EU Kids Act, is not yet reported, as the excerpt refers to a 'warning' during an ongoing legislative process. Attorneys advising online service providers, social media platforms, and educational technology companies should closely monitor the development of the EU Kids Act, paying particular attention to provisions concerning parental consent mechanisms, age verification protocols, and children's data rights. The Dutch government's intervention suggests that the final text may incorporate more robust safeguards for children's autonomy and privacy, potentially moving beyond a simplistic parental consent model. Practitioners should prepare to advise clients on adapting their privacy policies, terms of service, and age-appropriate design principles to comply with what could be stricter and more nuanced regulations aimed at protecting children online.

30 Oct
United States
Legal News

CrowdStrike: AI Cyberattacks on Law Firms Double, Threatening Legal Sector

Researchers warned on October 30, 2026, that law firms and other legal entities globally are experiencing a significant increase in cyberattacks leveraging agentic artificial intelligence, with such attacks doubling since 2023, according to cybersecurity company CrowdStrike's 2026 Legal Threat Landscape Report. The report, released on Wednesday (presumably October 28, 2026), indicates a 39% increase in legal entities named as hacking targets between August 2025 and August 2026, totaling 455. CrowdStrike's Senior Vice President for Counter Adversary Operations, Adam Meyers, noted the "democratization of hacking" through agentic technology, predicting the situation will worsen before improving. While CrowdStrike did not name specific victims, Reuters reported breaches at Quinn Emanuel Urquhart & Sullivan, Wilmer Cutler Pickering Hale and Dorr, and Seyfarth Shaw in recent months. This trend poses a critical threat to client confidentiality, data integrity, and the operational continuity of legal practices, making it highly significant for practitioners. Law firms, by their nature, handle highly sensitive and valuable information, including privileged communications and proprietary business data, making them prime targets for sophisticated adversaries. The increasing use of AI in these attacks suggests a more advanced and rapidly evolving threat landscape, requiring enhanced and proactive defensive strategies. Breaches can lead to severe reputational damage, significant regulatory fines under various data protection regimes, and substantial professional liability claims, impacting both the firm and individual attorneys. The legal profession operates under strict ethical obligations regarding client confidentiality, such as those outlined in ABA Model Rule 1.6, which mandates competence in technology and reasonable efforts to prevent unauthorized access to client information. Furthermore, various data privacy regulations, including the GDPR, CCPA, and numerous state-specific breach notification laws, impose significant compliance burdens and potential penalties for data breaches. The increasing sophistication of AI-driven attacks necessitates a re-evaluation of existing cybersecurity frameworks, compliance measures, and professional responsibility standards within law firms, pushing the boundaries of what constitutes "reasonable efforts" in data protection. Key parties involved in highlighting this issue include cybersecurity company CrowdStrike, which published the 2026 Legal Threat Landscape Report, and its SVP Adam Meyers. The ABA Journal and Reuters are the sources reporting on these developments, with Reuters specifically naming law firms like Quinn Emanuel Urquhart & Sullivan, Wilmer Cutler Pickering Hale and Dorr, and Seyfarth Shaw as having experienced cyber breaches. The broader legal community, including all law firms and legal departments, are the primary stakeholders and potential targets of these evolving threats. Attorneys and legal professionals must prioritize robust cybersecurity measures, including advanced threat detection systems, regular employee training on AI-driven phishing and social engineering tactics, and comprehensive incident response planning. Firms should regularly audit their systems, consider specialized legal tech cybersecurity solutions, and stay abreast of evolving AI-powered threats and defensive strategies. Proactive risk management, continuous investment in cybersecurity infrastructure, and strict compliance with data protection regulations are paramount to mitigate the severe financial, reputational, and ethical consequences of a data breach in this increasingly hostile digital environment.

30 Oct
Kenya
Legal News

KARMA Warns: Poor Records Threaten Kenya AI Systems' Reliability

The Kenya Association of Records Managers and Archivists (KARMA) has warned in Kenya that poor records management could undermine the adoption and reliability of Artificial Intelligence (AI) in government and business operations, potentially leading to unreliable outcomes and compromised decision-making. This significant development highlights that the efficacy of AI systems in the Kenyan context is directly contingent upon the quality and integrity of the underlying data. KARMA, through its Secretary General Collins Mutimba, emphasized that incomplete, inaccurate, or poorly secured records could severely compromise AI-generated information, thereby undermining critical decision-making processes, accountability frameworks, and the delivery of public services as organizations accelerate their digital transformation efforts. The warning comes ahead of KARMA's 10th Annual Records Management Conference, themed "AI-Ready Records for Smart Content-Based Governance," which underscores the growing concern among professionals regarding information quality and security in the age of automated systems. For legal practitioners and businesses in Kenya, this warning carries substantial legal significance. It underscores the critical need for robust data governance frameworks and meticulous records management as foundational prerequisites for any successful and legally compliant AI implementation. The reliability of AI outputs, which may inform business strategies, regulatory compliance, or even legal evidence, is directly at risk if the source data is flawed. This issue touches upon principles of data protection, such as those enshrined in Kenya's Data Protection Act, 2019, which mandates data accuracy and integrity, and also implicates broader administrative law principles concerning accountability and transparency in public service delivery. The courts, regulators, and various government and private sector entities involved in AI adoption will increasingly scrutinize the data provenance and quality underpinning AI-driven decisions. Key parties involved in this discourse include the Kenya Association of Records Managers and Archivists (KARMA) and its Secretary General Collins Mutimba, who are advocating for improved standards. The warning is directed at Kenyan government institutions and businesses that are either adopting or considering AI technologies. The upcoming conference will bring together professionals from government, the private sector, academia, and international institutions, indicating a broad stakeholder engagement on this critical issue. Attorneys advising clients on AI adoption in Kenya should prioritize conducting thorough data quality audits and establishing comprehensive information governance policies before any AI system deployment. They must ensure that clients' records management practices comply with existing data protection laws and best practices to mitigate legal and reputational risks associated with unreliable AI outcomes. Businesses, in turn, must view investment in proper records management, digitization, and data quality as an indispensable component of their AI strategy, rather than an afterthought, to ensure that their AI initiatives are both effective and legally sound.

30 Oct
Senegal
Courtroom Update

Senegal: Tahirou Sarr Nourah Cybersecurity Investigation Escalates

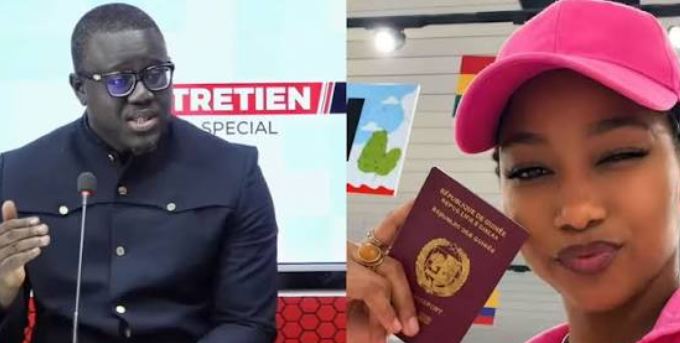
In Senegal, Mariama Ba, widely known as Nourah, who is already under judicial detention in connection with a separate legal proceeding, is now facing two additional complaints filed by Deputy Tahirou Sarr and Thierno Birahim. These new complaints have been formally transmitted by the public prosecutor's office to the Special Cybersecurity Division (DSC) for thorough investigation. The excerpt indicates that Nourah's legal challenges are escalating, with these new actions adding to her existing judicial burdens. The specific nature of the allegations contained within these two new complaints, or the alleged actions by Nourah that prompted them, are not detailed in the provided information, nor is any outcome or specific charge reported. This development carries significant legal implications, particularly highlighting the increasing prevalence of cyber-related offenses and the specialized investigative capabilities within the Senegalese legal framework. The involvement of the Special Cybersecurity Division strongly suggests that at least one of the new complaints pertains to digital misconduct or offenses committed through information and communication technologies. For legal practitioners, this underscores the growing importance of expertise in cybersecurity law and the complexities of defending individuals facing multiple, concurrent legal proceedings, especially when one is already in pre-trial detention. It also signals a robust response from the authorities to alleged digital transgressions. The legal context for these new complaints would involve Senegal's laws on cybercrime, which address a range of offenses from online defamation and harassment to other forms of digital malfeasance. The fact that Nourah is already subject to a "mandat de dépôt" (pre-trial detention order) indicates she is facing serious charges in her initial case, and these new complaints will undoubtedly complicate her legal position. The Senegalese judicial system, through the public prosecutor's office and specialized units like the DSC, is actively engaged in processing and investigating such complaints. The specific statutes under which these new complaints are brought are not specified in the excerpt, but they would fall under the relevant cybercrime legislation. Attorneys representing individuals, particularly those in the public eye or with a significant online presence, must be acutely aware of the legal risks associated with digital interactions and content. They should advise clients on proactive measures to ensure compliance with cybercrime laws and prepare for potential investigations by specialized units like the DSC. For businesses, this case serves as a reminder of the need for robust internal policies regarding digital conduct and data security. The ongoing nature of this matter, with no reported outcomes for the new complaints, necessitates close monitoring by legal professionals for insights into the application of cybercrime laws and judicial processes in Senegal.

30 Oct

Privacy & Data Protection coverage by jurisdiction

Other topics