
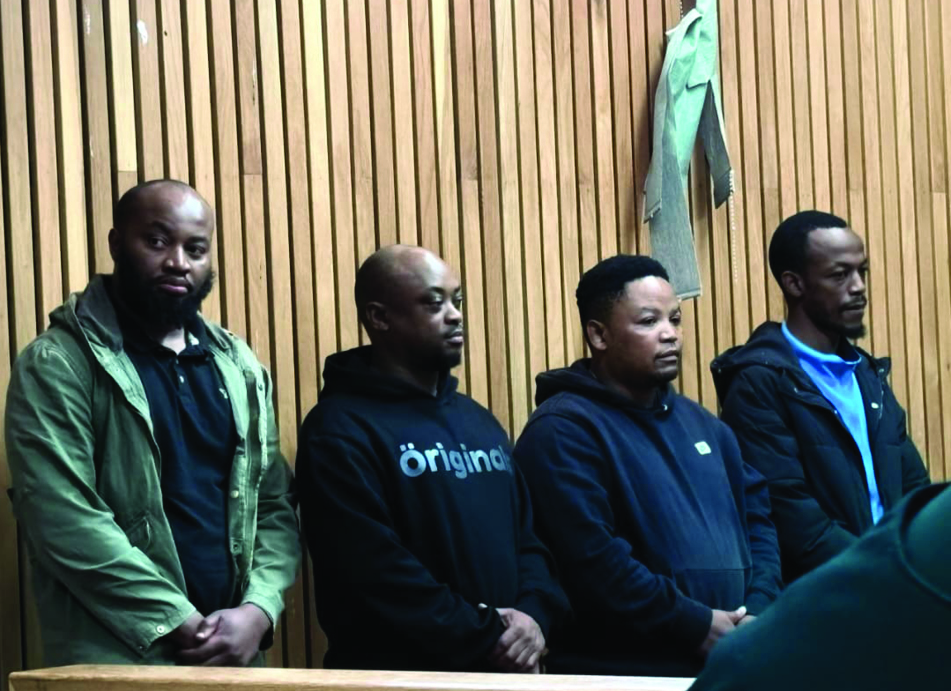
Standard Bank Eswatini: Cyber Fraud Bail Granted for Employee
Summary
- A Standard Bank Digital Consultant, Thabiso Easter Sihlongonyane, faces charges in an alleged E396,000 digital banking fraud.
- Sihlongonyane and three co-accused were granted E50,000 bail by Judge Nkosinathi Maseko.
- The alleged fraud involved compromising a customer's online banking credentials and performing a SIM card swap.
- This Eswatini cybercrime fraud case highlights vulnerabilities in financial institutions regarding internal controls and digital security.
What Happened
This particular Eswatini cybercrime fraud case, involving a Standard Bank employee, underscores the persistent and evolving threat of internal cyber fraud within financial institutions.
A digital consultant employed by Standard Bank Eswatini, Thabiso Easter Sihlongonyane, has been granted bail in connection with an alleged E396,000 digital banking fraud. This significant Eswatini cybercrime fraud case also saw three co-accused receive bail. The allegations center on the compromise of a customer's online banking credentials and the subsequent execution of a SIM card swap, a method often used to gain unauthorized access to financial accounts.
The alleged scheme involved sophisticated tactics to illicitly access funds. The core of the accusation against Sihlongonyane, a Standard Bank employee, and the co-accused, points to a breach of security protocols that allowed for the manipulation of a customer's mobile number. This manipulation, specifically a SIM card swap, is a critical element in the alleged E396,000 digital banking fraud, enabling the perpetrators to bypass security measures tied to the customer's phone.
Legal Context
The decision to grant bail was made by Judge Nkosinathi Maseko, who set the bail amount for Sihlongonyane and the three co-accused at E50,000 each. This ruling came despite the serious nature of the allegations, which directly implicate a bank employee in a substantial cyber fraud. The court's determination to allow bail underscores specific legal considerations in the Eswatini justice system, even when faced with accusations of significant financial crime and sophisticated digital manipulation.
The granting of bail by Judge Nkosinathi Maseko in this Standard Bank Eswatini cyber fraud bail case highlights the judicial process balancing the rights of the accused against the gravity of the alleged offenses. Despite the claims involving a Standard Bank employee and the use of a SIM card swap to facilitate the E396,000 digital banking fraud, the court found grounds to release the individuals on the stipulated bail amount. This outcome sets a precedent for how similar cybercrime cases might be handled in the future within the jurisdiction.
Why It Matters
This particular Eswatini cybercrime fraud case, involving a Standard Bank employee, underscores the persistent and evolving threat of internal cyber fraud within financial institutions. The alleged involvement of a digital consultant, a role typically requiring access to sensitive systems and customer information, raises critical questions about internal controls and the vulnerabilities inherent in digital banking platforms. The method of a SIM card swap banking fraud in Eswatini further illustrates how criminals exploit the intersection of telecommunications and banking security.
The implications extend beyond the immediate financial loss, pointing to a broader challenge for compliance officers and cybersecurity protocols. The fact that a Standard Bank employee is facing fraud charges in connection with a E396,000 digital banking fraud, facilitated by a SIM card swap, emphasizes the need for robust internal safeguards and continuous monitoring of employee access to sensitive data. For legal professionals, this case provides a recent example of bail being granted in a significant cyber fraud proceeding in Eswatini, which could be relevant for similar future proceedings, offering insights into judicial approaches to such complex digital crimes.
Practical Implications
This case highlights the ongoing threat of internal cyber fraud within financial institutions, particularly involving digital consultants and methods like SIM card swaps. Compliance officers should review their internal controls and cybersecurity protocols to mitigate risks associated with employee access to sensitive customer data and online banking systems. For lawyers, it provides a recent example of bail being granted in a significant cyber fraud case in Eswatini, which could be relevant for similar future proceedings.
Source
How does this affect you?
Get an AI analysis of this article grounded in your jurisdictions, practice areas, and any policy documents you've uploaded to Wansom.
Finish Reading the Full Story and the Expert Analysis.
Wansom is AI and can make mistakes.