
Eswatini Standard Bank Employee: Faces Cybercrime Charges in Pensioner Fraud
Summary
- A Standard Bank employee, Thabiso Esther Sihlongonyane, faces four charges under the Computer Crime and Cybercrime Act of 2022.
- She is accused of being part of a syndicate that allegedly defrauded a 66-year-old pensioner of E396,152.
- Sihlongonyane recently appeared at the Manzini Magistrate’s Court alongside three co-accused.
- The case highlights concerns about internal fraud and cybersecurity within Eswatini's financial institutions.
Recent Court Proceedings
This incident underscores the critical need for robust internal controls and cybersecurity protocols to prevent employee-perpetrated cybercrime and fraud.
A Standard Bank employee, Thabiso Esther Sihlongonyane, has recently been brought before the Manzini Magistrate’s Court in Eswatini, facing serious allegations related to a significant financial fraud. Sihlongonyane is accused of being a participant in a syndicate that allegedly orchestrated the defrauding of a 66-year-old pensioner. The reported loss to the elderly victim amounts to E396,152, a substantial sum that underscores the severity of the alleged crime. This case has drawn attention to the issue of internal fraud within financial institutions in the country.
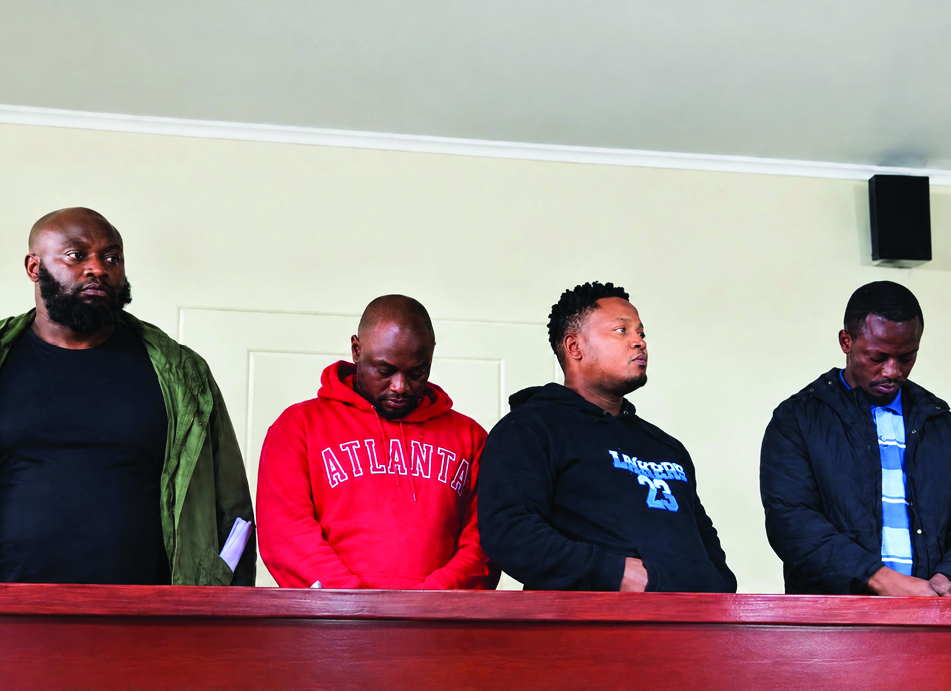
During her recent appearance before Principal Magistrate Florence Msibi, Ms. Sihlongonyane was formally charged with four counts. These charges fall under the stringent provisions of the Computer Crime and Cybercrime Act of 2022, indicating the digital nature of the alleged offenses. She did not appear alone, as three co-accused were also present in court, suggesting a coordinated effort behind the alleged scheme. The proceedings at the Manzini Magistrate’s Court mark a crucial step in addressing these serious allegations of financial misconduct.
Legal Framework and Charges
The legal foundation for the charges against Thabiso Esther Sihlongonyane and her co-accused is the Computer Crime and Cybercrime Act of 2022. This legislation, enacted in Eswatini, specifically targets offenses committed through or involving computer systems and networks, making it highly relevant to cases of cybercrime and digital fraud. The four charges levied against the Standard Bank employee highlight the breadth of activities covered by the Act, which aims to combat modern forms of financial malfeasance that exploit technological vulnerabilities.
The application of the Computer Crime and Cybercrime Act of 2022 in this Manzini Magistrate’s Court fraud case signals the authorities' commitment to prosecuting technologically-enabled financial crimes. For financial institutions like Standard Bank Eswatini, such cases underscore the evolving legal landscape and the increased scrutiny on their digital security measures. The Act provides a robust framework for addressing complex fraud schemes that might involve manipulating banking systems or exploiting customer data, emphasizing the need for strict compliance and preventative measures.
Implications for Financial Security
This particular incident of pensioner fraud in Eswatini financial institutions serves as a stark reminder of the vulnerabilities faced by elderly clients and the potential for significant financial exploitation. The alleged E396,152 loss to the 66-year-old victim is not merely a monetary figure but represents a profound breach of trust and potentially life-altering financial damage. Such cases of internal fraud within banking systems erode public confidence and necessitate immediate and comprehensive responses from the sector.
For Standard Bank Eswatini, and indeed all financial entities, this case of Eswatini Standard Bank employee cybercrime charges underscores the critical need for robust internal controls and cybersecurity protocols to prevent employee-perpetrated cybercrime and fraud. It highlights that even with external security measures, the risk of internal collusion or misuse of access remains a significant challenge. Compliance officers must meticulously review existing safeguards, while legal counsel should advise on potential liabilities under the Computer Crime and Cybercrime Act of 2022, ensuring that both preventative and responsive strategies are in place to mitigate future risks.
Practical Implications
This case underscores the critical need for financial institutions in Eswatini to bolster internal controls and cybersecurity protocols to mitigate risks of employee-perpetrated cybercrime and fraud. Compliance officers should review existing safeguards, while legal counsel should advise on potential liabilities under the Computer Crime and Cybercrime Act.
Source
How does this affect you?
Get an AI analysis of this article grounded in your jurisdictions, practice areas, and any policy documents you've uploaded to Wansom.
Finish Reading the Full Story and the Expert Analysis.
Wansom is AI and can make mistakes.