
ESCCOM Warns Businesses on Cyberattack, AI Safety Risks
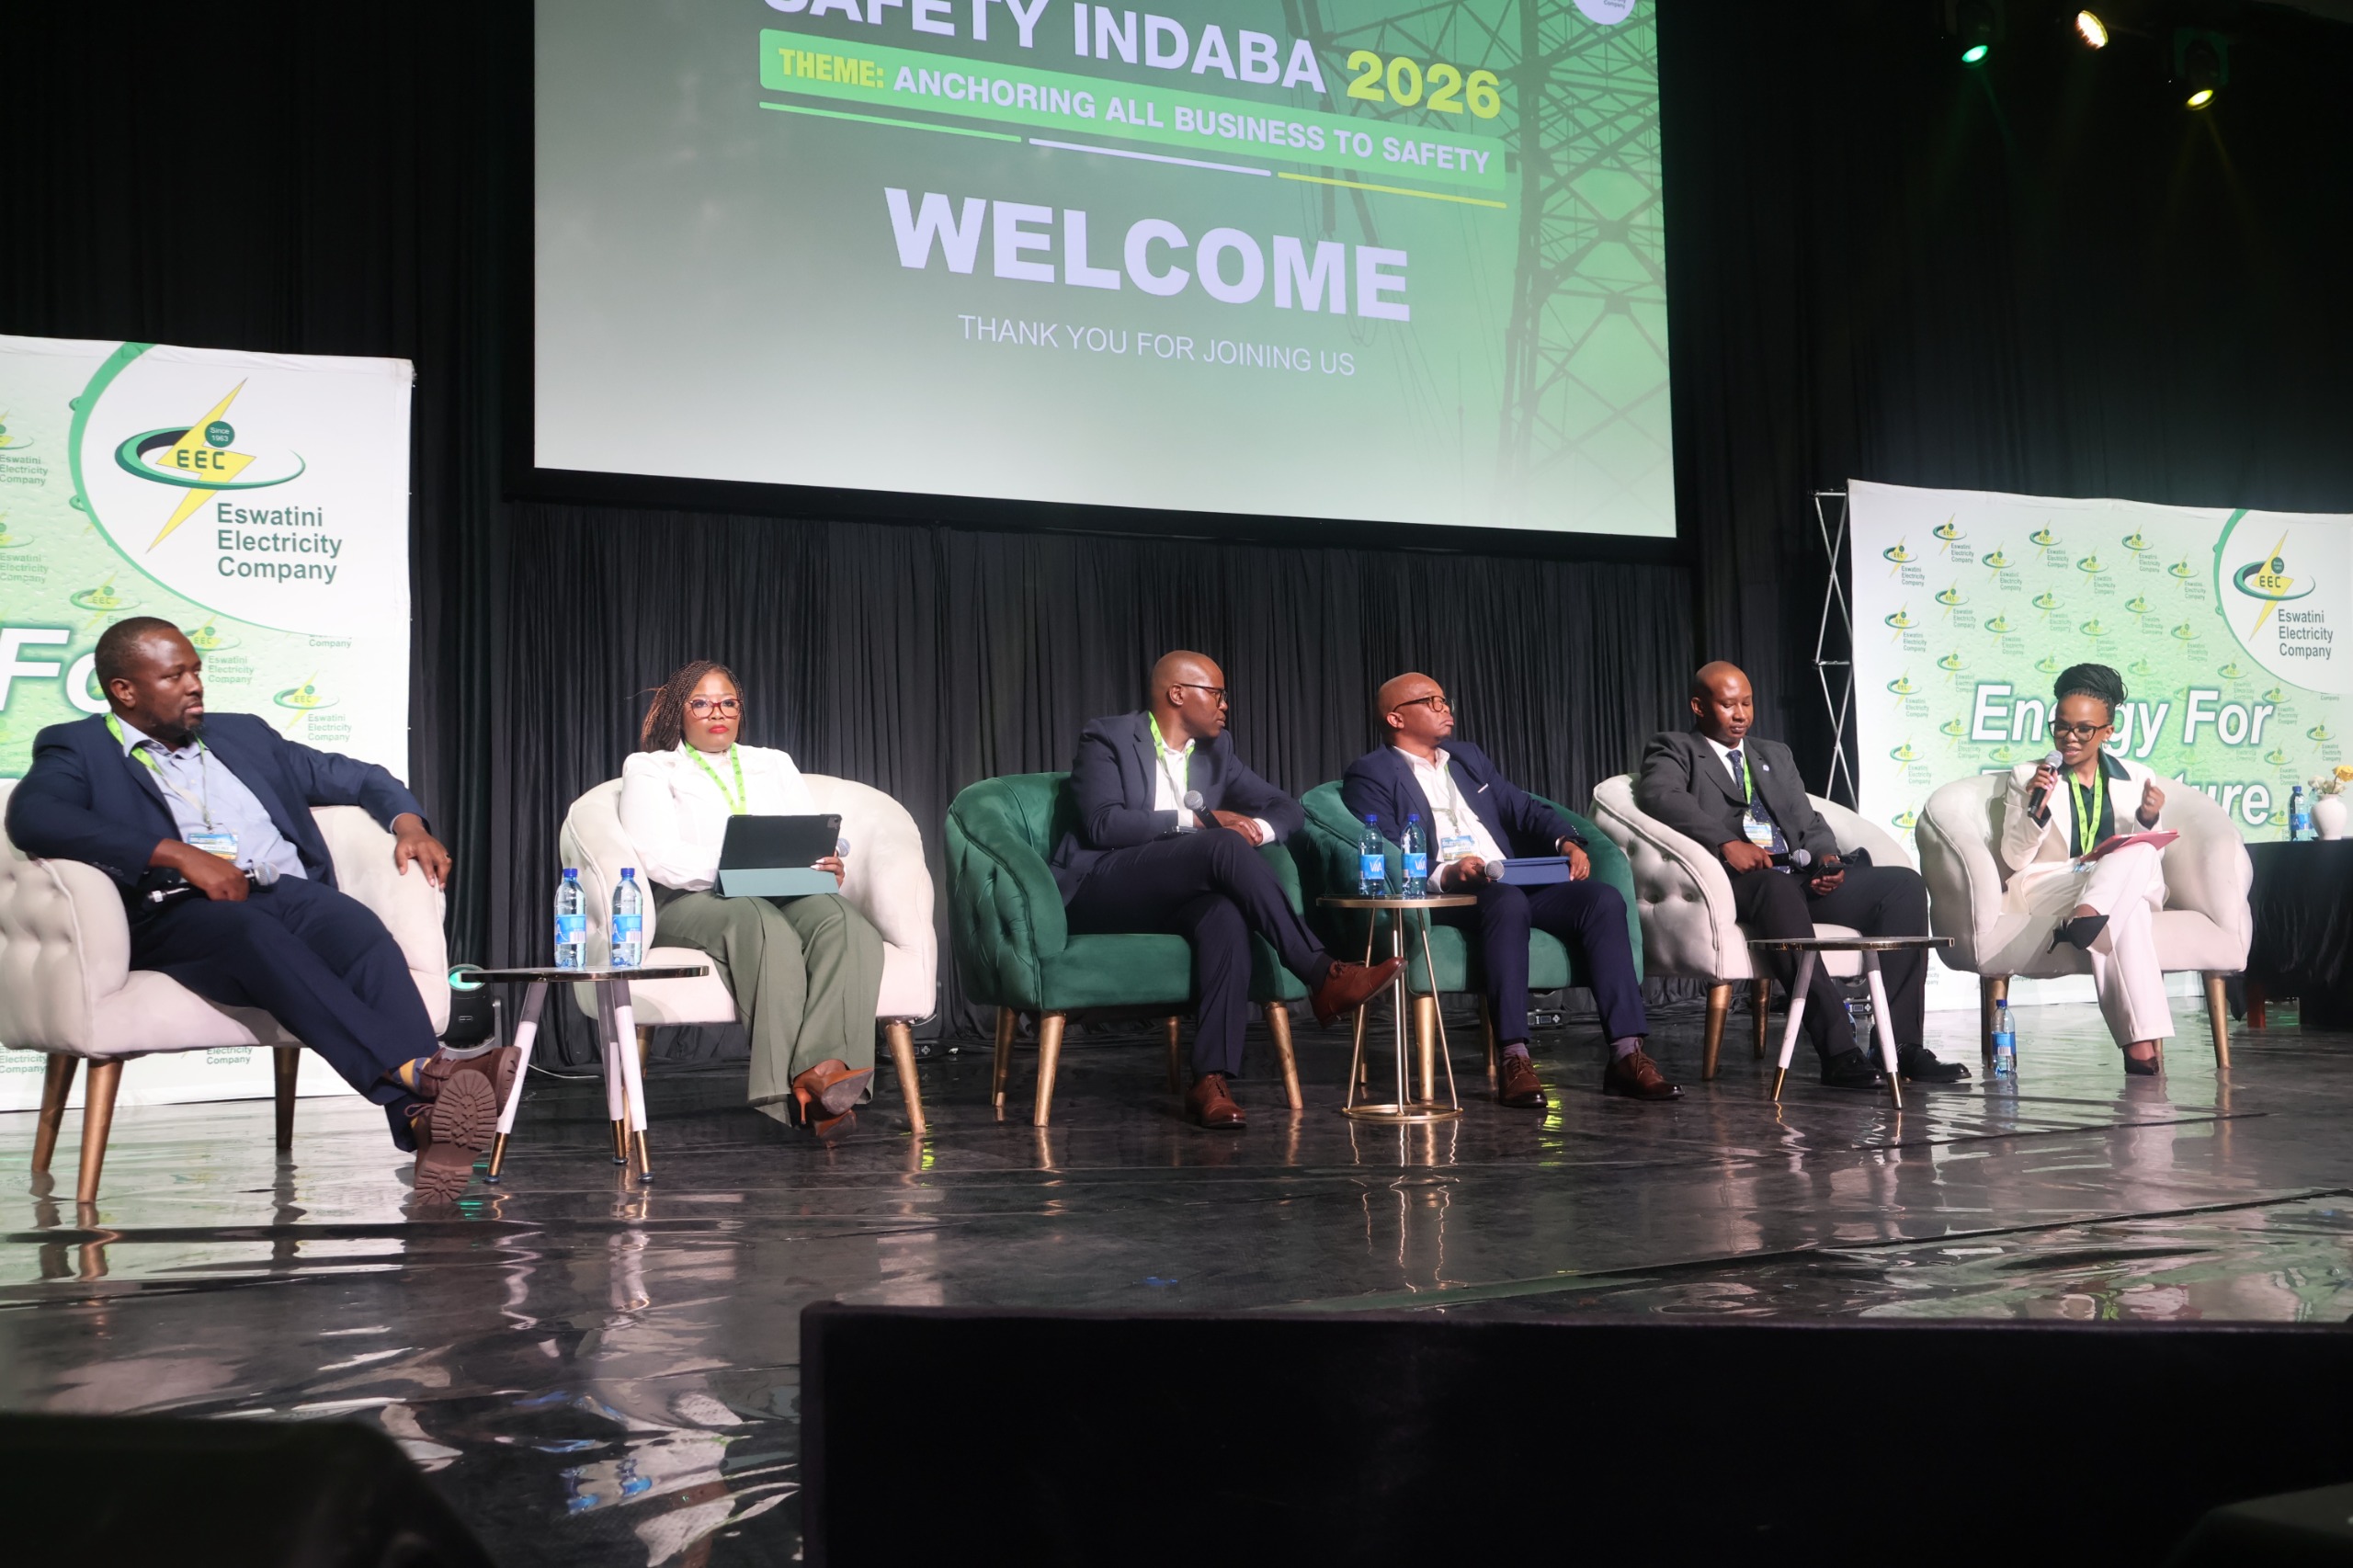
Samuelson Shongwe from the Eswatini Communications Commission (ESCCOM) warned businesses in Eswatini about new safety risks, including cyberattacks and artificial intelligence, during a panel discussion on business safety in Sidvokodvo.
This development is legally significant as it signals a growing regulatory focus on digital risks within Eswatini, pushing businesses to expand their understanding of safety beyond physical premises to encompass cyber resilience and data protection. For legal practitioners, it underscores an expanding area of law requiring expertise in technology, data privacy, and regulatory compliance. The increasing reliance on technology means businesses face heightened legal liabilities for data breaches, system failures, and the misuse of AI, making robust legal advice on preventative measures and incident response critical.
The legal context for these warnings is rooted in Eswatini's evolving legislative landscape concerning technology and data. While the excerpt does not specify particular statutes, the Electronic Communications Act, 2013, provides a foundational framework for digital interactions. However, the discussion points to the urgent need for more specific legislation addressing cybercrime, data protection (akin to the Protection of Personal Information Act in South Africa or GDPR internationally), and potentially the ethical governance of artificial intelligence. ESCCOM, as the communications regulator, is a key player in shaping and enforcing these standards, making its pronouncements highly relevant for compliance.
Key parties involved include Samuelson Shongwe representing the Eswatini Communications Commission (ESCCOM), which serves as the primary regulator for communications and digital services in the country. The warnings are directed at businesses operating within Eswatini, which are increasingly dependent on digital systems and data. The panel discussion itself serves as a platform for raising awareness and influencing corporate governance practices.
Attorneys should proactively advise their business clients on the imperative of conducting comprehensive cybersecurity risk assessments, developing robust data protection policies, and implementing incident response plans. They must stay abreast of any new or proposed legislation related to cybercrime, data privacy, and AI governance in Eswatini. Businesses should be encouraged to invest in legal audits of their technological infrastructure and data handling practices to mitigate potential legal and reputational risks arising from cyber threats and the responsible deployment of AI.
How does this affect you?
Get an AI analysis of this article grounded in your jurisdictions, practice areas, and any policy documents you've uploaded to Wansom.
Finish Reading the Full Story and the Expert Analysis.
Get the latest legal & regulatory intelligence in Eswatini
Wansom is AI and can make mistakes.