
South Africa ITAM Compliance Demands: Critical Governance Needed
Summary
- Effective IT asset management (ITAM) governance is crucial for organizations to reduce compliance exposure and strengthen security controls in South Africa.
- South African legislation, including POPIA, the Cybercrimes Act, the Companies Act, and King V, mandates responsible and ethical technology asset use.
- Many organizations still lack robust ITAM governance, relying on outdated methods or having poor visibility into their IT assets, leading to significant compliance, audit, and security risks.
- Global surveys indicate that a substantial portion of organizations lack accurate visibility into their on-premises hardware and software.
- V-Track offers advisory services, tailored policies, and audit preparation to help organizations, especially small and mid-sized ones, address ITAM governance gaps and align with frameworks like ITIL and COBIT.
The Growing Imperative for Robust ITAM Governance
As digital footprints expand and cybercrime intensifies globally, poorly managed or uncontrolled IT assets present significant vulnerabilities, serving as potential entry points for malicious actors.
Organizations across all sectors are facing increasingly stringent South Africa ITAM compliance demands, making robust IT asset management (ITAM) governance a critical priority. Effective ITAM frameworks are instrumental in mitigating compliance exposure, bolstering security protocols, and ensuring that technology assets are managed responsibly throughout their entire lifecycle, from acquisition to disposal. Despite its escalating importance, ITAM governance is frequently overlooked, a concern highlighted by Valene Nagiah, Head of Asset Tracking and Management at V-Track.
As digital footprints expand and cybercrime intensifies globally, poorly managed or uncontrolled IT assets present significant vulnerabilities, serving as potential entry points for malicious actors. Concurrently, the regulatory landscape and best-practice guidelines are evolving, placing greater emphasis on organizations to demonstrate ethical, compliant, and responsible utilization of their technological resources. This dual pressure underscores the urgent need for a strategic re-evaluation of existing ITAM practices.
South Africa's Evolving Regulatory Landscape
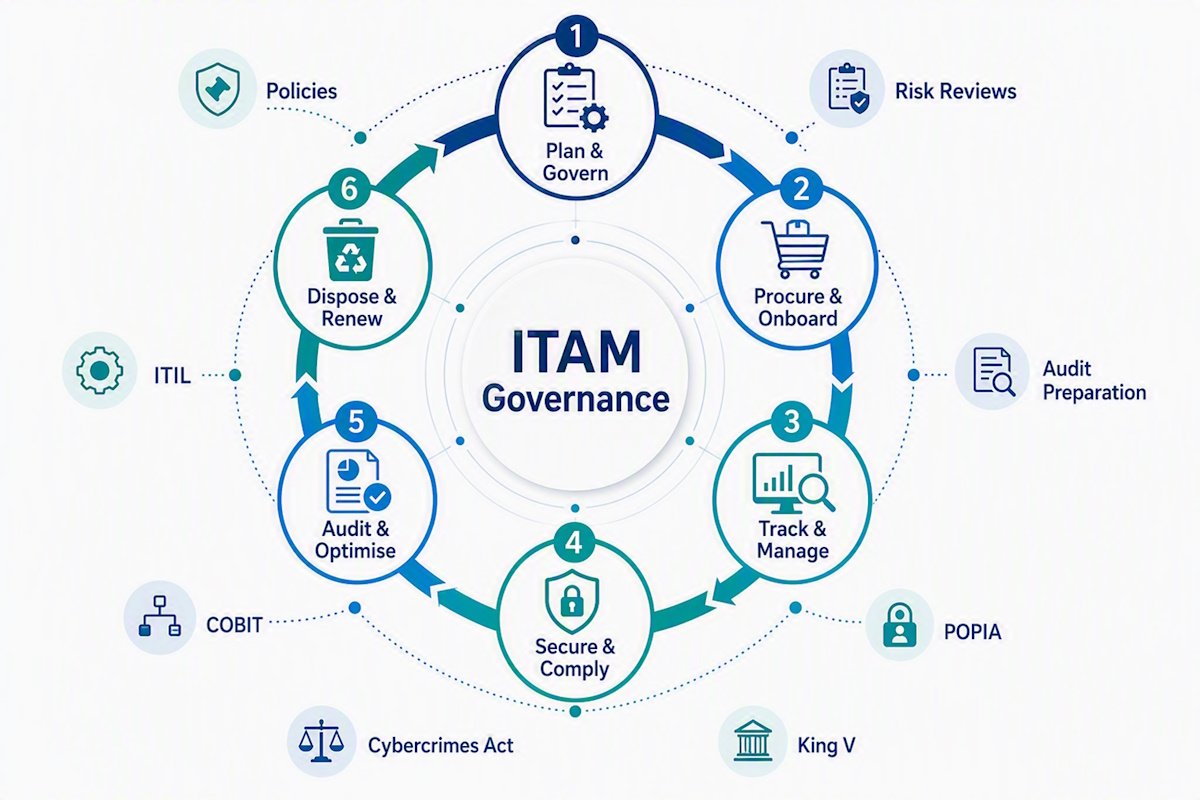
The heightened significance of ITAM governance is clearly reflected in South Africa's legislative and governance frameworks. Key regulations such as the Protection of Personal Information Act (POPIA IT asset management), the Cybercrimes Act (Cybercrimes Act ITAM ZA), the Companies Act, and the King V Report on Corporate Governance collectively reinforce the necessity for organizations to implement effective, compliant, and ethical processes for the acquisition, development, use, and distribution of technology. According to Nagiah, this means establishing comprehensive policies, standards, and frameworks that govern the entire procurement, management, utilization, and eventual disposal of IT assets.
To aid organizations in formalizing these essential controls, recognized governance structures like ITIL and COBIT offer valuable guidance. ITIL provides practical methodologies for managing IT services and assets across their lifecycle, helping entities enhance value, control costs, and effectively manage risks associated with the purchase, use, and disposal of IT assets. Similarly, COBIT, developed by ISACA, offers a broader governance and management framework for enterprise information and technology, assisting organizations in aligning technology governance with stakeholder needs, optimizing risk, managing resources efficiently, and monitoring performance. These ITIL COBIT ITAM frameworks are crucial for navigating complex compliance requirements.
Persistent Gaps and Escalating Risks
Despite a general awareness among organizations regarding the necessity for up-to-date ITAM governance frameworks, many still fall short in implementation. This disconnect creates significant ITAM compliance risk South Africa. A global perspective from Flexera's 2026 State of ITAM survey revealed that only 74% of organizations believe they possess accurate visibility into their on-premises hardware, with a slightly higher 78% reporting visibility into their on-premises software across increasingly complex IT environments.
In the South African context, Nagiah observes that a considerable number of organizations continue to rely on outdated policies or procedures, basic spreadsheet-based asset registers, or entirely lack formal ITAM governance structures. This absence of clear policies and processes exposes them to escalating compliance, audit, and security risks, making them vulnerable to regulatory penalties and cyber threats.
Strategic Support for Robust ITAM Frameworks
Addressing these critical governance gaps requires specialized expertise and tailored solutions. V-Track, an intelligent IT asset tracking solution offered by InnoVent, provides comprehensive support for ITAM governance. This includes developing tailored IT asset policies, conducting thorough risk reviews, and offering audit preparation services designed to help organizations close their governance deficiencies.
This support is particularly beneficial for small and mid-sized organizations that may not possess the internal resources or specialized knowledge required to manage complex ITAM compliance demands effectively. V-Track ITAM advisory services assist organizations in defining and preparing core policies and procedures across a wide array of key areas, including IT asset lifecycle management, hardware and software asset management, software compliance, mobile device management, acceptable use policies, IT asset disposal, audit preparation and processes, and employee onboarding and off-boarding processes related to IT assets. These services also focus on establishing ITAM governance structures specifically designed to reduce business risk and ensure alignment with recognized IT governance structures such as ITIL and COBIT.
Practical Implications
Lawyers and compliance officers in South Africa should advise clients to urgently review and strengthen their IT asset management (ITAM) governance frameworks. This is crucial to mitigate compliance exposure and legal risks under POPIA, the Cybercrimes Act, Companies Act, and King V, which increasingly demand responsible technology asset use.
Source
Source: Original reporting via ITWeb
How does this affect you?
Get an AI analysis of this article grounded in your jurisdictions, practice areas, and any policy documents you've uploaded to Wansom.
Finish Reading the Full Story and the Expert Analysis.
Get the latest legal & regulatory intelligence in South Africa
Wansom is AI and can make mistakes.