
Cyber security is everyone’s problem. Here’s how to build a security culture that lasts
Summary
- Cybersecurity training in corporate South Africa is often ineffective due to a one-off, compliance-focused approach, leaving organizations vulnerable.
- Effective strategies require treating cybersecurity as a 'people problem,' with strong leadership, personalized content, and tailored training for different departments.
- A layered training framework includes baseline awareness, role-specific content, scenario-based learning, and regular refreshers, ideally informed by annual risk profiling.
- Artificial intelligence offers benefits for training personalization and scale but carries risks, particularly employees inadvertently exposing sensitive data through AI interactions.
- Organizations must balance AI's capabilities with human oversight, ensuring AI-driven training is relevant to real-world scenarios to avoid flawed guidance and mitigate risks.
South Africa's Cybersecurity Training Imperative
When security principles are deeply integrated into the operational fabric of a business, they become an inherent part of daily processes and decision-making, moving beyond the realm of isolated interventions.
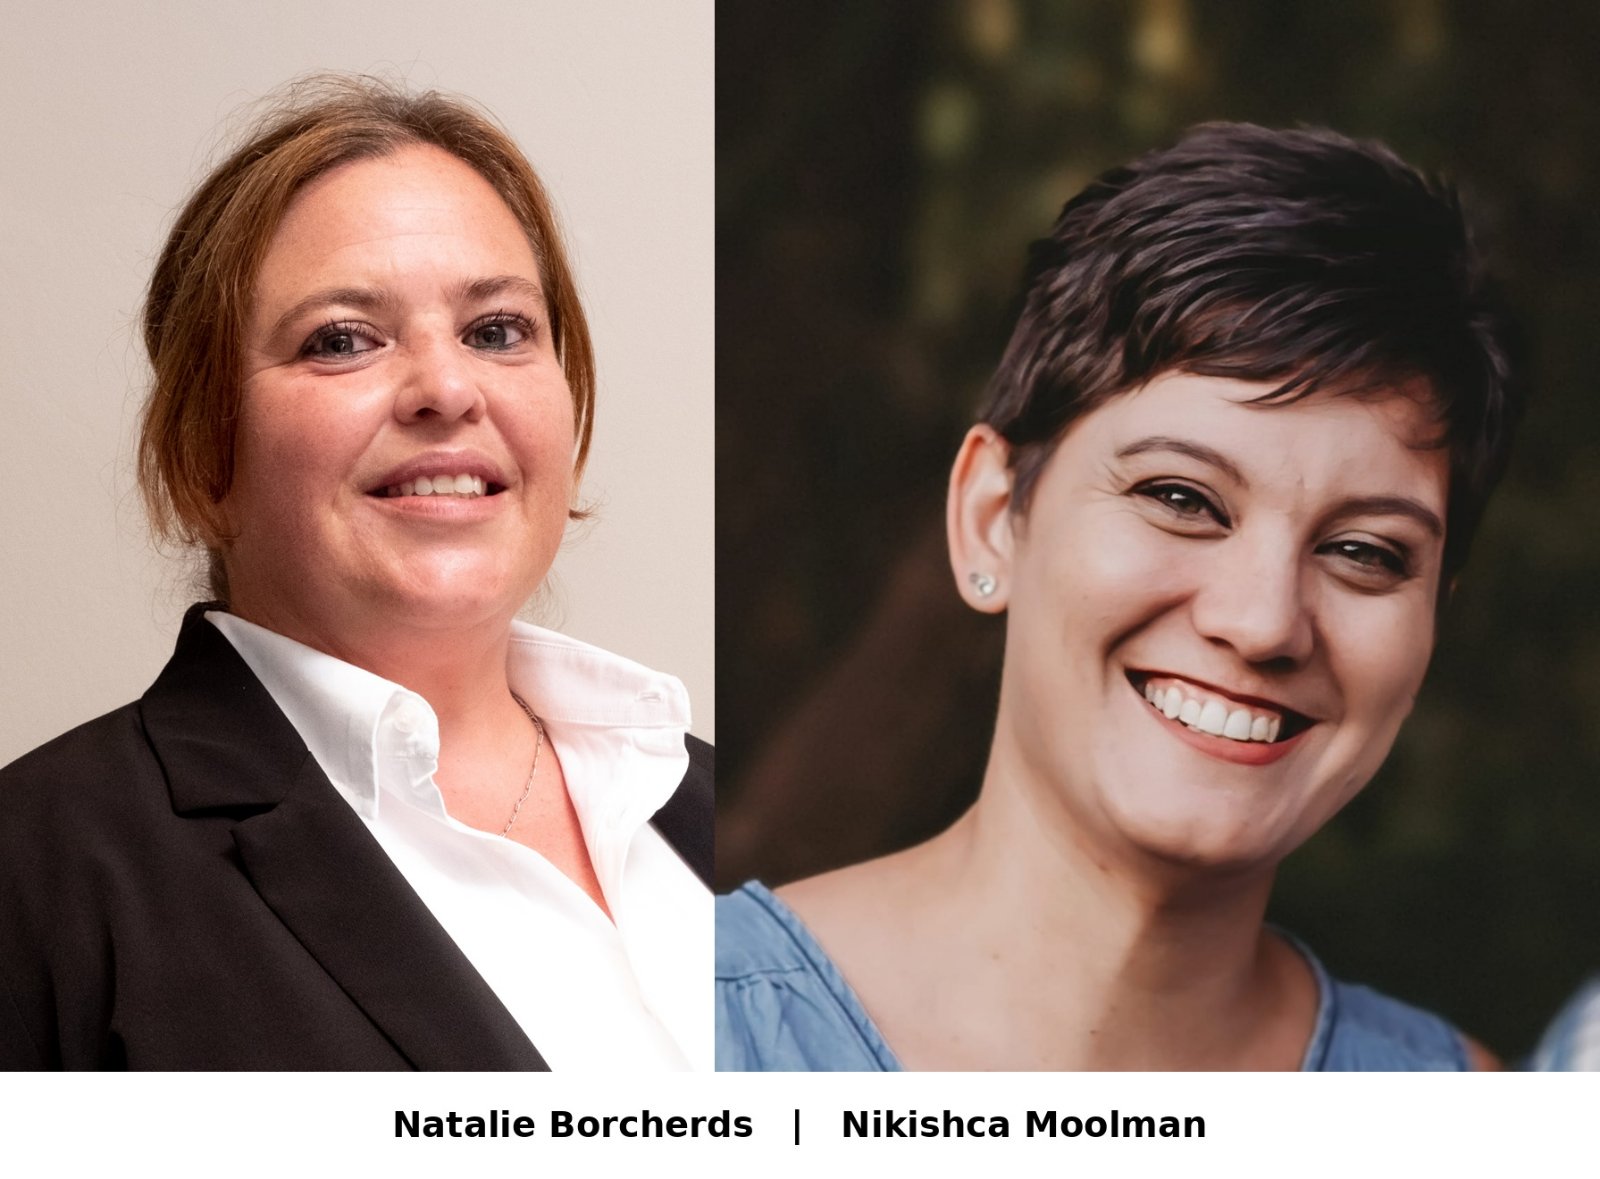
Corporate entities in South Africa frequently encounter a persistent challenge in cybersecurity training, not due to a lack of investment, but rather an approach that often treats it as a one-time, box-ticking exercise. This superficial engagement means employees quickly forget crucial information, while evolving threats leave organizations continuously exposed to vulnerabilities. The prevailing view among experts, including Nikishca Moolman, an Information Security Consultant at Galix, is that successful organizations shift their focus from viewing cybersecurity solely as a technological problem to recognizing it as a human one.
This fundamental shift is critical for developing an effective South Africa corporate cybersecurity culture strategy. When security principles are deeply integrated into the operational fabric of a business, they become an inherent part of daily processes and decision-making, moving beyond the realm of isolated interventions. This perspective underscores that a robust security posture is less about sophisticated software and more about the informed actions and awareness of every individual within an organization.
Cultivating a Proactive Security Mindset
Building a resilient security culture begins at the top, with leadership visibly championing cybersecurity initiatives. Executive endorsement sends a clear message throughout the organization, and how leaders respond to security incidents—with support rather than reprimand—reinforces the idea of shared responsibility. Beyond leadership, personal relevance is a powerful motivator. Natalie Borcherds, Security Services Manager at Galix, highlights that when individuals understand how cyber threats can impact their personal lives, families, and finances, abstract work requirements transform into personal priorities. Real-world examples, often drawn from social media habits or daily interactions, help employees connect abstract lessons to tangible threats, fostering genuine behavioral changes.
A common pitfall in building security culture ZA is a generic, one-size-fits-all training approach. Different departments face distinct threat landscapes; for instance, finance teams are prime targets for phishing and fraud, HR handles sensitive employee data, and IT manages critical infrastructure. Moolman emphasizes that treating all teams identically is a recipe for failure. Instead, tailored cyber awareness programs South Africa should reflect these specific risks. She advocates for a layered training framework: universal baseline education on password hygiene and phishing, role-specific content aligned with departmental tools and risks, scenario-based learning to illustrate consequences, and regular refreshers to keep pace with an ever-changing threat environment. Annual risk profiling at the departmental and role level is recommended to ensure training remains relevant, as one cannot manage what is not understood. This approach does not necessarily demand expensive bespoke systems; organizations can leverage real-world incidents from the news and existing tools to develop effective Galix South Africa cybersecurity training.
Leveraging AI Responsibly in Training
Artificial intelligence is revolutionizing the delivery of security training by enabling personalized content, realistic threat simulations, and scalable awareness programs across large workforces. However, experts like Moolman caution that AI can be both a valuable asset and a significant liability. A primary concern, often overlooked by organizations, involves the inadvertent exposure of sensitive data by employees interacting with AI tools. Seemingly innocuous actions, such as uploading documents, describing workflows, or sharing personal details, contribute to a growing digital footprint that AI systems can utilize in unforeseen ways. Moolman warns that "everything you do leaves a footprint on the internet," highlighting the potential for AI systems to quietly leverage this information.
Borcherds further advises that AI-driven training must be grounded in real-world scenarios pertinent to the organization, rather than relying on generic, algorithm-generated content. Over-reliance on automation can diminish human oversight, and poorly developed AI platforms may disseminate flawed guidance. The key lies in striking a balance: utilizing AI to broaden the reach and enhance the relevance of training while ensuring human judgment and oversight remain central to the process, thus mitigating AI cybersecurity training risks ZA.
Strategic Compliance and Risk Mitigation
For compliance officers and in-house counsel in South Africa, assessing an organization's cybersecurity training strategy against these best practices is paramount. A continuous, tailored, and leadership-driven approach is essential for enhancing data protection compliance and effectively mitigating legal risks stemming from cyber incidents. The insights from Galix experts underscore that a robust South Africa corporate cybersecurity culture strategy is not merely a technical undertaking but a strategic imperative that requires ongoing commitment and adaptation.
By embedding security awareness into the organizational DNA and ensuring training is relevant, personal, and continuously updated, businesses can significantly reduce their vulnerability. This proactive stance not only protects sensitive data and critical systems but also strengthens an organization's overall resilience against the evolving landscape of cyber threats, aligning with regulatory expectations and safeguarding against potential legal repercussions.
Practical Implications
Compliance officers and in-house counsel in South Africa should assess their organisation's cybersecurity training strategy against these best practices, particularly regarding continuous, tailored, and leadership-driven approaches, to enhance data protection compliance and mitigate legal risks from cyber incidents.
Source
Source: Original reporting via ITWeb
How does this affect you?
Get an AI analysis of this article grounded in your jurisdictions, practice areas, and any policy documents you've uploaded to Wansom.
Finish Reading the Full Story and the Expert Analysis.
Get the latest legal & regulatory intelligence in South Africa
Wansom is AI and can make mistakes.