
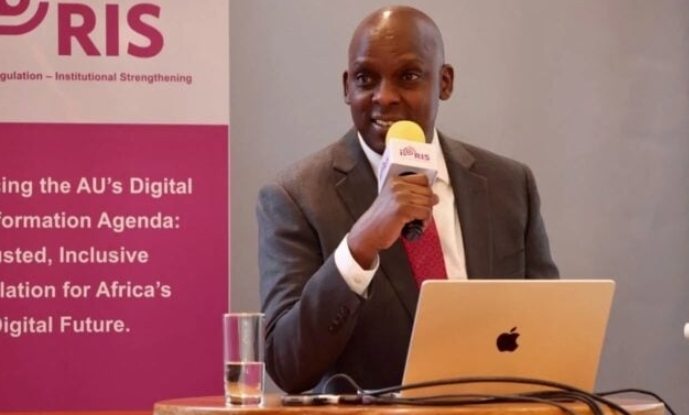
African ICT Regulators: Cross-Border Cyberthreats Forum Calls for Unity
Summary
- Technology experts, policymakers, and partners convened in Nairobi to discuss cyber threats.
- A unified approach among Africa's regulators was strongly advocated to combat cross-border cyber risks.
- The forum highlighted that a damaged submarine cable can disrupt commerce across a dozen countries.
- Sophisticated fraud schemes devised in one location can impact multiple nations.
- Participants emphasized the necessity of African regulatory cooperation to enhance cybersecurity across the continent.
What Happened
Lawyers and compliance officers must recognize this increased focus on multi-jurisdictional cyber risk and proactively prepare their clients for evolving compliance requirements.
A significant gathering of technology experts, policymakers, and various affiliated partners recently took place in Nairobi, the capital city, on Monday. The primary focus of this assembly was to address the escalating challenge of cyber threats that transcend national borders across the African continent. During this Regional ICT Regulators’ Forum, a unified consensus emerged, underscoring the critical need for African regulators to collaborate more closely.
Participants at the forum collectively advocated for enhanced cooperation and a cohesive strategy among the continent's regulatory bodies. This concerted effort is deemed essential for developing effective mechanisms to counter the sophisticated and often multi-jurisdictional nature of modern cyber attacks. The discussions highlighted that individual national responses are insufficient against threats that do not respect geographical boundaries, necessitating a continent-wide approach to digital security.
The Pervasive Nature of Cross-Border Cyberthreats
The forum underscored the intricate and far-reaching impact of cyber incidents, illustrating how a single event can trigger widespread disruption across multiple nations. For instance, the discussions pointed out that damage to a submarine cable off the coast of one country has the potential to significantly impede commerce and communication across as many as a dozen other countries. This highlights the physical infrastructure's vulnerability and its cascading effects on regional economies.
Furthermore, the experts detailed how sophisticated fraud schemes, often originating in one jurisdiction, can rapidly propagate and affect individuals and businesses across numerous African states. Such examples serve to emphasize the interconnectedness of digital infrastructure and financial systems, making a localized response to cybercrime largely ineffective. The pervasive nature of these threats necessitates a robust, coordinated defense mechanism that spans national borders.
The Imperative for Regulatory Harmonization
The call for unity among Africa's ICT regulators is a direct response to this complex threat landscape, advocating for African regulatory cooperation cyber. This initiative aims to foster a more harmonized approach to cybersecurity policies and enforcement across the continent. The participants at the Nairobi forum stressed that aligning regulatory frameworks is crucial for building a resilient digital environment capable of withstanding sophisticated cross-border attacks.
Achieving African cyber security harmonization would not only streamline incident response protocols but also create a more predictable legal and operational environment for businesses and citizens. This collaborative effort seeks to overcome the challenges posed by differing national laws and technical standards, which can often be exploited by malicious actors. The forum's emphasis on unity signals a strategic shift towards a collective security posture against digital adversaries.
Implications for Legal and Compliance Professionals
For legal and compliance professionals, the outcomes of such regional forums, including the recent Regional ICT Regulators’ Forum Nairobi, are increasingly vital to monitor. The discussions signal a growing momentum towards the potential harmonization of cyber security laws and cross-border data protection Africa regulations across various African jurisdictions. This development will inevitably reshape the compliance landscape for entities operating within or across these nations.
Lawyers and compliance officers must recognize this increased focus on multi-jurisdictional cyber risk and proactively prepare their clients for evolving compliance requirements. This includes adapting to new regulations concerning cross-border data flows, enhancing incident response capabilities, and understanding the implications of harmonized cybercrime laws East Africa. The proactive engagement with these emerging regulatory trends is essential for mitigating legal and operational risks in an increasingly interconnected digital Africa.
Practical Implications
Lawyers and compliance officers should monitor the outcomes of such regional forums for potential harmonization of cyber security laws and data protection regulations across African jurisdictions. This signals an increased focus on multi-jurisdictional cyber risk and the need for clients to prepare for evolving compliance requirements related to cross-border data flows and incident response.
Source
How does this affect you?
Get an AI analysis of this article grounded in your jurisdictions, practice areas, and any policy documents you've uploaded to Wansom.
Finish Reading the Full Story and the Expert Analysis.
Get the latest legal & regulatory intelligence in Rwanda
Wansom is AI and can make mistakes.