
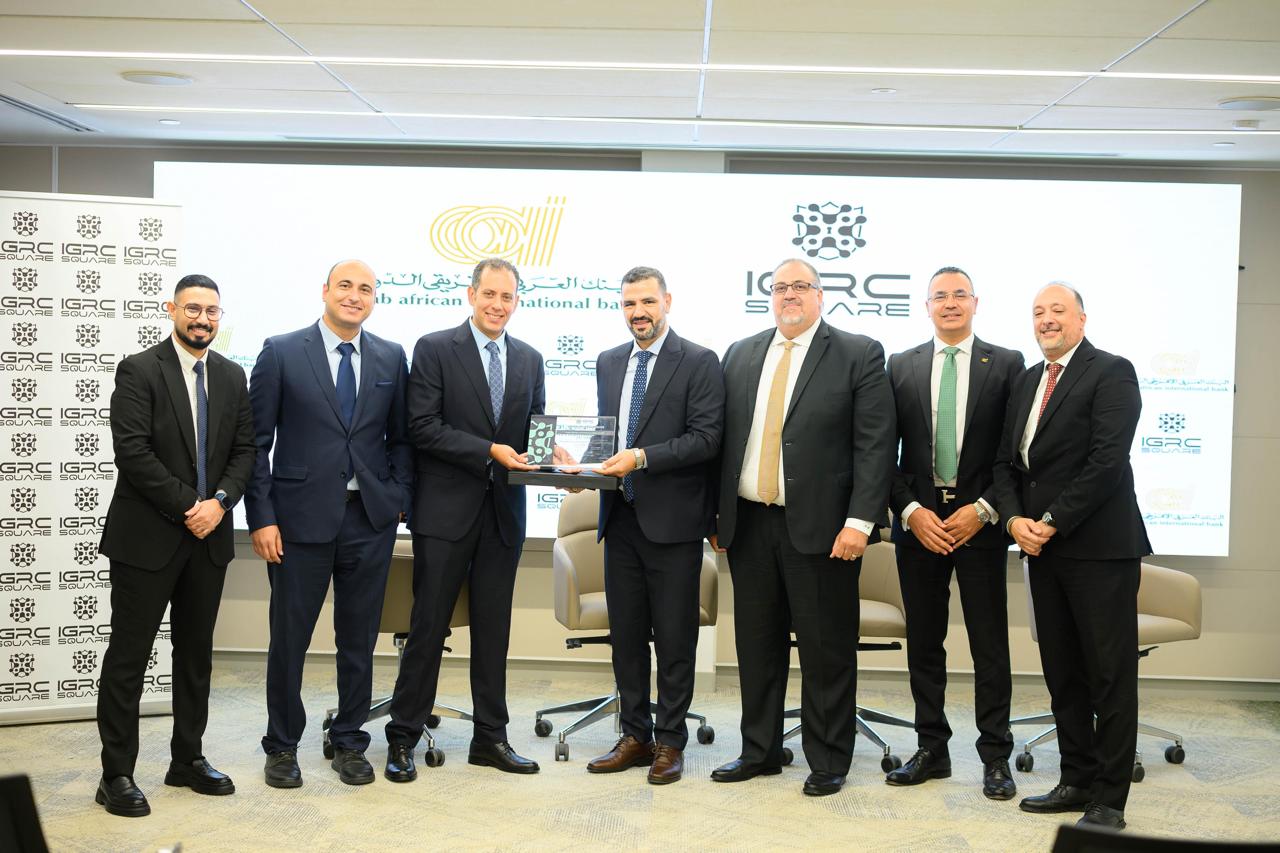
AAIB: Secures PCI DSS v4.0.1 Certification in Egypt
Summary
- Arab African International Bank (AAIB) has obtained the latest PCI DSS v4.0.1 certification.
- The certification aims to protect customer payment data and strengthen card transaction security.
- Achieving this standard required AAIB to implement a comprehensive set of security measures.
- This AAIB PCI DSS v4.0.1 certification in Egypt sets a new benchmark for data security in the market.
- The development may influence regulatory expectations and best practices for cybersecurity in other Egyptian financial institutions.
What Happened
Compliance officers in other Egyptian financial institutions should take note of this certification, as it potentially influences regulatory expectations and shapes best practices for mitigating cybersecurity risks across the industry.
Arab African International Bank (AAIB) has successfully secured the latest version of the Payment Card Industry Data Security Standard (PCI DSS v4.0.1) certification, a significant milestone announced by the bank itself. This achievement directly reflects AAIB's strategic objective to enhance the security of card transactions and ensure the robust protection of its customers' payment data. The rigorous process of obtaining the AAIB PCI DSS v4.0.1 certification in Egypt necessitated the implementation of a comprehensive and advanced set of security measures, aligning the bank with the most current global standards for payment card security.
This certification underscores AAIB's proactive stance in addressing the evolving landscape of digital threats. By adopting PCI DSS v4.0.1, the bank reinforces its commitment to maintaining the highest levels of cybersecurity for its cardholders. This move is integral to safeguarding sensitive financial information and upholding trust in the bank's payment processing infrastructure, positioning AAIB as a leader in secure financial services within the region.
Legal and Industry Context
The Payment Card Industry Data Security Standard (PCI DSS) represents a critical global framework designed by major payment card brands to ensure the secure handling of cardholder data throughout its lifecycle—from processing and storage to transmission. The recent update to PCI DSS v4.0.1 introduces more stringent requirements and refined best practices, reflecting the dynamic nature of cybersecurity threats and technological advancements. For financial institutions operating in Egypt, such as Arab African International Bank, achieving PCI DSS v4.0.1 compliance is not merely a technical compliance checkbox but a fundamental requirement for maintaining operational integrity and consumer confidence in the digital payment ecosystem.
This standard outlines a detailed set of controls spanning twelve key requirements, encompassing areas like network security, vulnerability management, access control, and the establishment of robust information security policies. The evolution to version 4.0.1 places a greater emphasis on continuous security monitoring and integration of security processes into daily business operations, moving beyond periodic assessments. For Egyptian banks, adhering to these rigorous international benchmarks is indispensable for seamless participation in global payment networks and for effectively countering sophisticated cyberattacks that frequently target payment card data, thereby bolstering overall Egyptian bank payment data security.
Why It Matters
The successful AAIB PCI DSS v4.0.1 certification in Egypt carries profound implications, not just for the bank but for the entire financial services sector in the country. This accomplishment by Arab African International Bank establishes a new, elevated benchmark for expected data security standards and robust payment card data protection within the Egyptian market. Consequently, compliance officers and risk managers in other Egyptian financial institutions should closely observe this development, as it is likely to influence regulatory expectations and shape best practices for mitigating cybersecurity risks across the industry.
This certification demonstrates AAIB's advanced capabilities in AAIB card transaction security and its unwavering commitment to enhancing Egyptian bank payment data security. By proactively adopting the latest version of the payment card industry data security standard, AAIB is effectively raising the bar for its competitors and highlighting the critical necessity for all entities that handle payment card information to continuously upgrade their security protocols. This investment in state-of-the-art cybersecurity measures is paramount for protecting sensitive customer information and ensuring the long-term integrity and resilience of Egypt's payment ecosystem.
Practical Implications
Compliance officers in other Egyptian financial institutions should note this certification as it sets a new benchmark for expected data security standards and robust payment card data protection within the market, potentially influencing regulatory expectations and best practices for mitigating cybersecurity risks.
Source
How does this affect you?
Get an AI analysis of this article grounded in your jurisdictions, practice areas, and any policy documents you've uploaded to Wansom.
Finish Reading the Full Story and the Expert Analysis.
Get the latest legal & regulatory intelligence in Egypt
Wansom is AI and can make mistakes.