
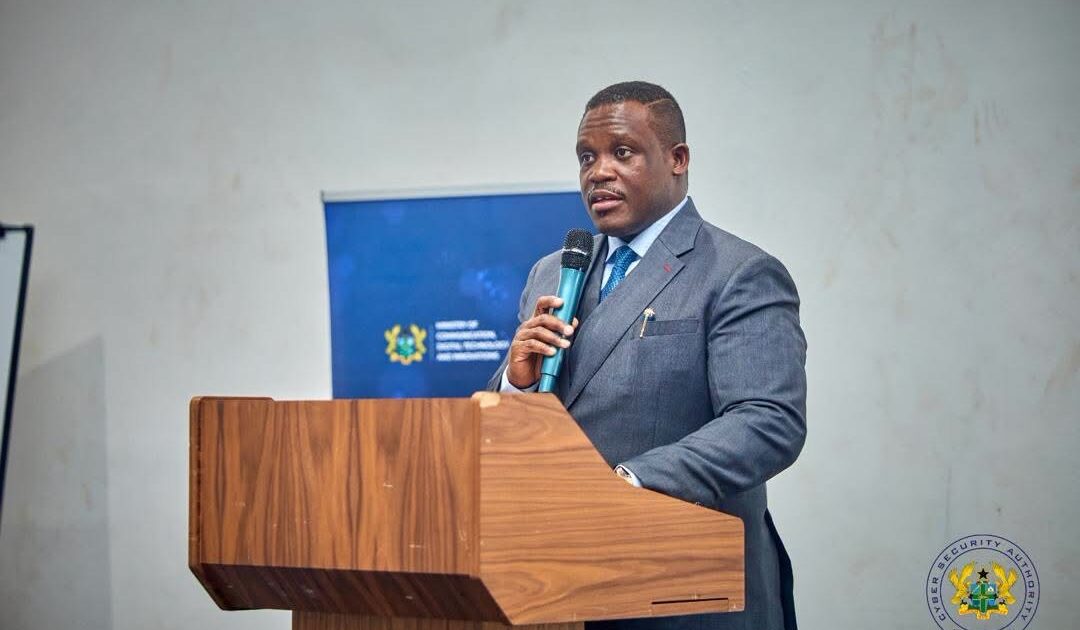
Samuel Nartey George: Mandates Ghana Critical Infrastructure Cybersecurity Compliance
Summary
- Samuel Nartey George, Minister for Communication, Digital Technology and Innovations, declared cybersecurity compliance mandatory for Ghana's Critical Information Infrastructure (CII) owners.
- The mandate, announced at a workshop during NCSAM 2026, emphasizes adherence to the Directive for the Protection of Critical Information Infrastructure.
- CII owners must strengthen governance, appoint accredited cybersecurity leadership, and ensure timely Ghana cybersecurity incident reporting.
- Regular audits and vulnerability assessments are required to identify and address weaknesses in critical systems.
- Owners are directed to engage only Tier 1 licensed cybersecurity providers Ghana for effective protection of critical infrastructure.
Ghana's Mandatory Cybersecurity Push
Owners of Critical Information Infrastructure (CII) in Ghana are now under a mandatory cybersecurity compliance regime, a directive underscored by Samuel Nartey George, the Minister for Communication, Digital Technology and Innovations.
Owners of Critical Information Infrastructure (CII) in Ghana are now under a mandatory cybersecurity compliance regime, a directive underscored by Samuel Nartey George, the Minister for Communication, Digital Technology and Innovations. Speaking at a workshop titled "CII Resilience Beyond IT: Securing Ghana’s Operational Technology Ecosystem," the Minister emphasized that adherence to these obligations is not optional but a fundamental requirement for responsible digital operations and the nation's overall resilience.
The workshop, held as part of National Cybersecurity Awareness Month (NCSAM) 2026, was a collaborative effort between the Ghana Cyber Security Authority CII and Cybershield. During the event, Minister George articulated that compliance with the Directive for the Protection of Critical Information Infrastructure Ghana is paramount. This clear statement from the Minister highlights the government's serious commitment to safeguarding essential digital assets and services across the country.
Key Obligations for Critical Infrastructure Owners
The Samuel Nartey George cybersecurity mandate outlines several specific actions that CII owners must undertake to meet their obligations. A primary requirement is to significantly strengthen existing cybersecurity governance frameworks, ensuring robust oversight and strategic direction for digital security initiatives. Furthermore, the Minister stressed the imperative of appointing accredited cybersecurity leadership within these organizations, guaranteeing that expert knowledge guides protection efforts.
Crucially, the mandate also includes a strict requirement for Ghana cybersecurity incident reporting to be conducted in a timely manner. This ensures that potential threats and breaches are addressed swiftly, mitigating broader impacts. CII owners are also expected to implement regular audits and comprehensive vulnerability assessments to proactively identify and rectify any weaknesses present in their critical systems, thereby enhancing their defensive posture against cyber threats.
Ensuring Robust Protection Through Licensed Providers
A significant component of the Minister's guidance for mandatory Ghana critical infrastructure cybersecurity compliance involves the selection of external cybersecurity service providers. Owners of Critical Information Infrastructure are explicitly instructed to engage exclusively with Tier 1 licensed cybersecurity providers Ghana. This measure is designed to ensure that the protection of Ghana's vital infrastructure is entrusted only to highly qualified, vetted, and officially recognized entities.
This strategic focus on licensed providers aims to elevate the standard of cybersecurity across critical sectors. By mandating the use of such providers, the government seeks to foster sustained compliance and embed strong, professional cybersecurity practices throughout the nation's essential digital infrastructure, reinforcing the overall security ecosystem.
The Broader Impact on National Resilience
The pronouncements by Minister George underscore a strategic national commitment to digital security, particularly concerning the nation's most vital systems. The emphasis on mandatory Ghana critical infrastructure cybersecurity compliance reflects a profound recognition of the escalating threats to essential services and critical data that underpin the country's functioning. This proactive stance is crucial for maintaining the integrity of public services, ensuring economic stability, and bolstering overall national security in an increasingly interconnected and vulnerable digital landscape.
By enforcing strict adherence to the Directive for the Protection of Critical Information Infrastructure Ghana, the nation aims to cultivate a resilient digital ecosystem. This framework is designed to be capable of withstanding sophisticated cyberattacks, thereby protecting citizens, businesses, and government operations from disruption and harm, ultimately contributing to a more secure and stable digital future for Ghana.
Practical Implications
Lawyers and compliance officers advising owners of Critical Information Infrastructure (CII) in Ghana must ensure their clients are aware of and actively implementing the mandatory cybersecurity obligations, including strengthening governance, appointing accredited leadership, timely incident reporting, and engaging Tier 1 licensed providers, to mitigate compliance risks under the Directive for the Protection of Critical Information Infrastructure.
Source
How does this affect you?
Get an AI analysis of this article grounded in your jurisdictions, practice areas, and any policy documents you've uploaded to Wansom.
Finish Reading the Full Story and the Expert Analysis.
Get the latest legal & regulatory intelligence in Ghana
Wansom is AI and can make mistakes.